
Bypass Google Two-Factor Authentication
Hey Folks, today’s article is going to be very interesting because we are going to talk about a method using which we can easily bypass “ Google Two Factor Authentication ” by tricking the victim. Let
This technique does not break Google's two-factor authentication cryptographically. It is osint concept in cybersecurity. It describes techniques, risks, or controls that defenders and ethical hackers must understand to protect systems and conduct authorized security testing. Learning Social Engineering helps you recognize attacks in the wild and apply industry-standard mitigations aligned with frameworks like OWASP and NIST.">social engineering: an attacker who already has your password tricks you into approving or forwarding the real login prompt within seconds. Below is how the method works — and, more importantly, how to defend against it, because the same steps show you exactly what an attacker needs you to do.
Hey Folks, today’s article is going to be very interesting because we are going to talk about a method using which we can easily bypass “Google Two Factor Authentication” by tricking the victim.
Let’s move on to the main topic !!
Get Credentials First
What this attack actually requires
To bypass two factor authentication of any google account, you must first have the username and password of that account and you must also use phishing with social engineering to obtain the credentials. But the question is how do we do all this ? All this is very easy to do you just only have to use a tool called “Advphishing” and you can easily get the victim’s account username, password and even OTP by using fake WhatsApp numbers. Once the whole process is done, keep the credentials with you and be calm.

What are we going to do ?
How Google's 2FA prompt works
Usually when we try to login to our google account for the first time from google chrome, it makes us do some security process to find out whether that person is the right person or not. Google provides several features for us to successfully login to an account and all of them have a two factor authentication feature called “Tap on notification to continue” which contains the attacker’s device information that alerts the victim to not allow attacker to login into his account. So we just need to replace our device information with the victim’s device information that they are using and we will be able to defraud the victim. Hence in this tutorial you will learn how you will be able to bypass two factor authentication by tricking the victim.
footprinting-social-engineering">Footprinting ( Social Engineering )
How the technique works, step by step
The real steps start from here where we will now use social engineering techniques to capture the victim’s device information. It is very easy to achieve and for that we have a complete tutorial on it where you can go from here. Once the victim clicks on the link provided by you then you will easily get every deep information about his device. What else do you want !! Copy it and HODL.

Enter the Credentials Found
Let’s go to the Google account and enter the credentials but after entering the password don’t submit it.

Set Fire to Burpsuite Tool
It is a web application penetration testing top leading tool which comes pre-installed in kali linux operating system which you need to open it but we can’t use it without setting proxy so you have to configure proxy first. Check this article if you got confused. Once everything is done, “Turn on” intercept mode and then go to google account and click on Next. The device information is always stored in the “User-Agent” param which we need to replace with the victim device information found from the footprinting. Let’s change it.
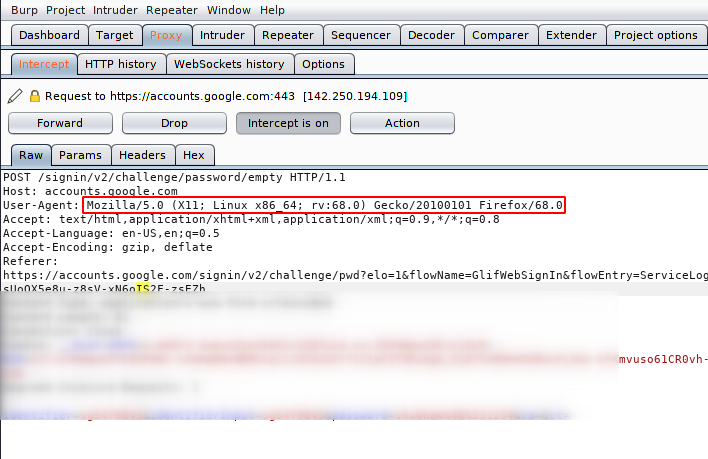
Good !! As you can see we have changed all the information as we got from the footprinting. After change it, forward the request.

Hmm !! Once again we have to follow the same process which we have done in our previous step. After change it then forward the request and “Turn off” the intercept the mode.
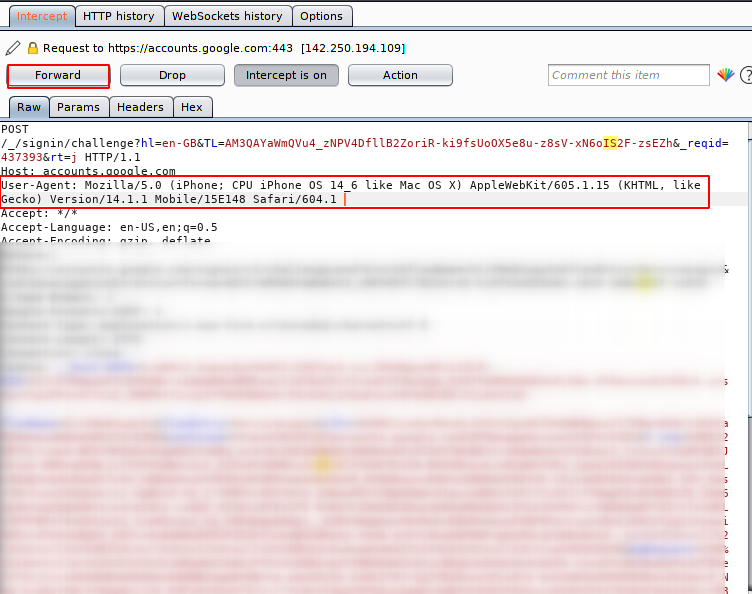
Note You have to do both these steps within nano seconds.
OMG !! As soon as you forward the request a notification alert will be sent to the victim phone and asking to allow this account to log in on the device the victim is using. Now the victim will think that the request must have come from my device and will allow him to login. BYPASSSSSSSS !!

Aamazing !! As you can see how easily we have taken over google account using social engineering techniques.
About the Author
Shubham Goyal Certified Ethical Hacker, information security analyst, penetration tester and researcher. Can be Contact on Linkedin.
How to defend against this attack
Because this method relies on you approving the login, the defence is to make that approval impossible to trick out of you. Switch from SMS or one-tap prompts to a phishing-resistant factor: a passkey or a hardware security key (FIDO2) is bound to the real Google domain and will not authenticate against an attacker's page. Turn on Google's sign-in alerts, and never approve a prompt you did not personally trigger — if a code or prompt arrives out of nowhere, someone already has your password, so change it immediately. Enrolling in Google's Advanced Protection Program enforces hardware keys and blocks exactly this class of social-engineering bypass.
Frequently Asked Questions
Can two-factor authentication be bypassed?
What is the safest way to secure a Google account?
Why is reverse-proxy phishing effective against 2FA?
Related Articles
Paywall Bypass
If you're trying to read an article behind a paywall, there are a few ways you can bypass it. One way is to use an Incog
ViewHow To Bypass OTP Using Burp Suite | OTP Bypass Using BurpSuite
Ever wondered how those pesky One-Time Passwords (OTPs) that safeguard our online accounts can be bypassed? Well, you're
ViewSeven Common Ways To Bypass Login Page
Hello to all beginner bug hunting fellows. This is Rocky, today i came with an another blog on login page. This blog is
ViewSSH DDoS Attack Simulation Using Python: A Comprehensive Guide
Hey guys! 👋 Rocky here. Let’s talk about something wild but super important: DDoS attacks targeting SSH —and how Python
ViewSocial Engineering Attack Life Cycle: The Art of Human Hacking
In the beginning, social engineering was an art of social science. It is used to change people’s behaviour and make chan
ViewCapture Android Traffic Remotely With Wireshark
As the world becomes increasingly mobile, capturing and analyzing Android traffic remotely has become a critical skill f
ViewCOMMENTS (0)
Sign in to post intel on this briefing.